Enterprise technology guide · Reviewed 11 October 2026
DPDP readiness starts with understanding how personal data moves through your existing systems. Map the journey from a website or app into your CRM, business applications and vendor tools. Then agree what needs to change, who owns each action and how your team will test it.
Choose one important customer journey. Follow it from data collection to downstream use and withdrawal. A focused walkthrough gives your IT, business and legal teams a concrete implementation brief instead of a vague request to “make everything compliant”.
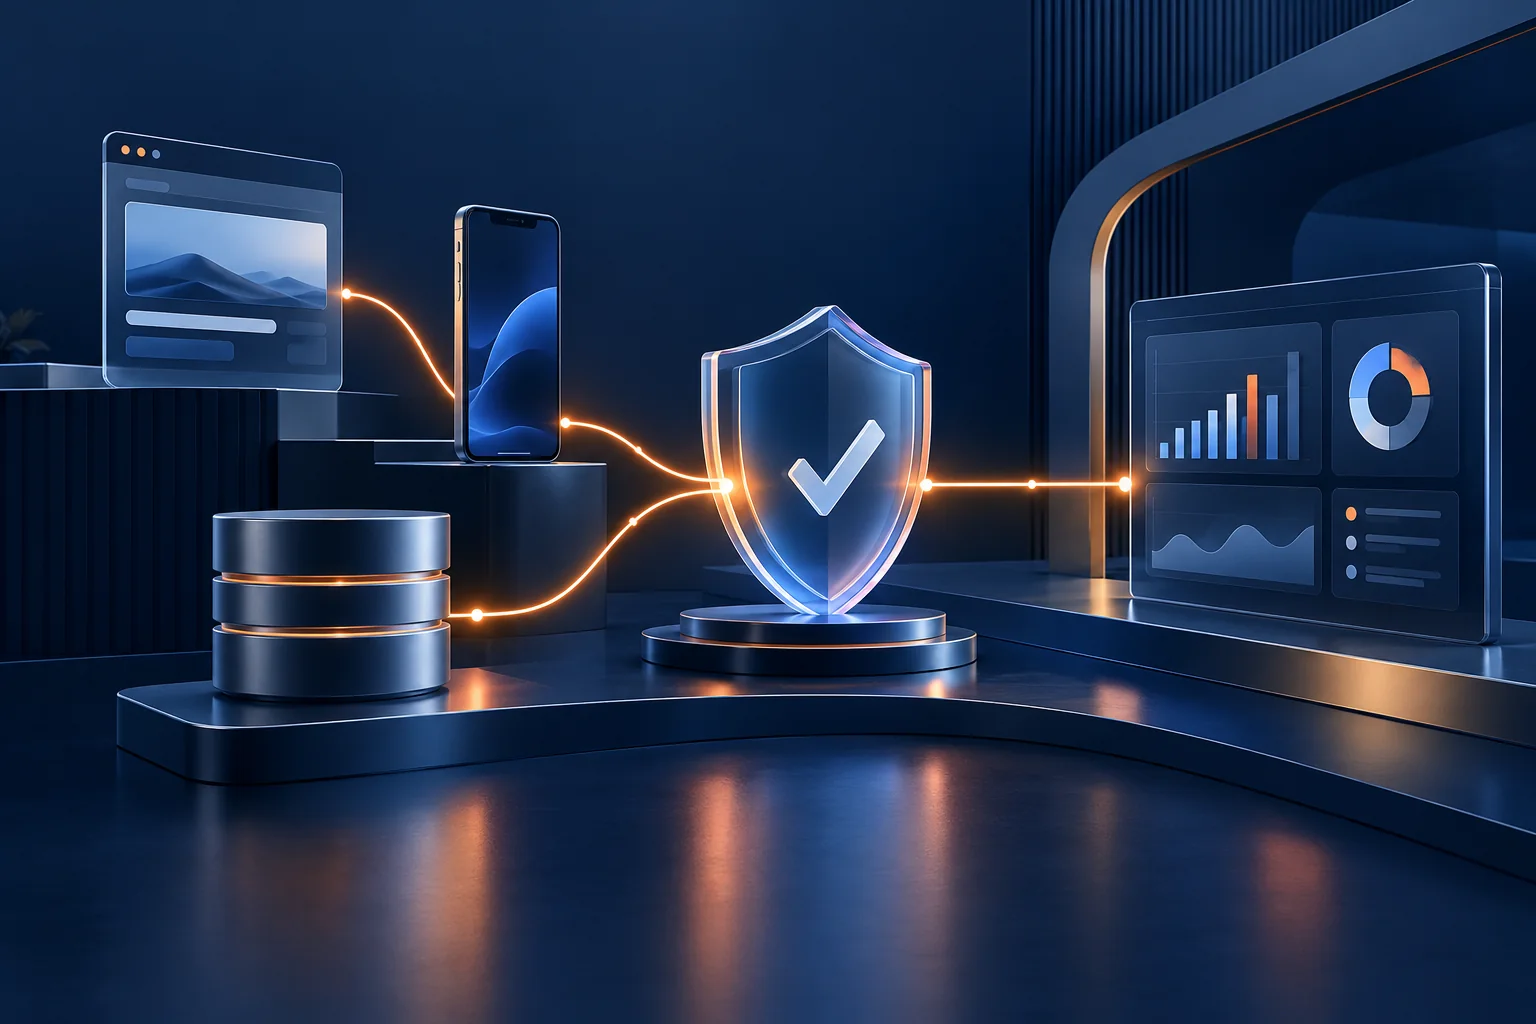
This guide is for Indian companies planning changes to websites, mobile apps, CRM and other business software. It explains a technical planning approach. Your legal or privacy adviser should determine applicability, processing grounds and the policies your software must implement.
Which DPDP dates should your project plan recognise?
The phase covering Consent Manager registration provisions. This is a distinct phase, not the general deadline for every company’s customer-data workflow.
The main phase covering core processing obligations and individual rights under the notified commencement schedule. Plan approvals, integration work and testing before this phase.
The official commencement notification specifies phased implementation. The government’s May 2026 statement also identifies 13 May 2027. Check subsequent notifications when approving your rollout.
Why an existing system needs a closer look
A company can have a working website, a reliable CRM and a useful mobile app while still having disconnected preferences. A change captured in one application may never reach a scheduled export, a campaign tool or a vendor queue.
The first question is operational: can your team follow a person’s choice through every relevant system? Do not assume a checkbox, a privacy policy link or a new software purchase answers that question.
Example: a preference changes, but the CRM does not
A customer withdraws a marketing choice in a portal. The portal saves the change, but the CRM still includes that customer in its next campaign export.
A scoped integration could pass the approved change to the CRM, confirm the result and flag failed updates for an owner to review. Your team must also decide which other tools receive the event and how conflicting records are handled.
Illustrative planning example; not a claim about any customer’s system or results.
A six-step existing-system readiness checklist
-
Map the journey and name the owner
List the forms, apps, CRM fields, exports and vendor tools involved in one use case. Include manual handoffs. Name the business owner and technical contact for each destination.
Working output: a data-flow map with named owners and unresolved questions.
-
Agree the purpose and approved wording
Ask your legal or privacy team to approve the purpose, relevant processing ground and notice content before building screens. Keep the approved version connected to the implementation brief.
Working output: an approved requirements sheet, including exceptions that need separate treatment.
-
Design the record you need to explain a choice
For consent-based journeys, consider how the system will connect a choice to an identity, purpose, notice version, time and capture channel. Define access controls and retention with the responsible team.
Working output: a sample record and a clear explanation of each field.
-
Connect changes to downstream applications
Check available APIs, identity matching and event handling. Decide how retries, duplicates and conflicting values are reviewed. Include spreadsheets and scheduled exports in the walkthrough.
Working output: an integration list with success checks and failure owners.
-
Test the difficult paths
Test more than a successful submission. Try a delayed CRM response, duplicate customer records, an unavailable vendor endpoint and a user returning after changing a preference.
Working output: agreed acceptance scenarios and evidence of the test results.
-
Plan handover and ongoing review
Give operations staff a way to review failed actions. Document who approves future notice changes, monitors integrations and updates the implementation when systems or requirements change.
Working output: a rollout plan, owner checklist and maintenance scope.
What should each corporate team bring?
| Team | Useful input for the project |
|---|---|
| IT and engineering | System inventory, API access, authentication approach, identity matching and deployment constraints. |
| Business operations | Real customer journeys, manual exports, task ownership and the review process for failed actions. |
| Legal and privacy | Applicability, approved purposes and notices, processing grounds, retention and exception decisions. |
| Security | Access controls, monitoring, security review and incident-response dependencies. |
Understand the penalties without turning them into a sales claim
The Act’s Schedule provides ceilings of ₹250 crore for security-safeguard breaches, ₹200 crore for breach-notification failures, ₹200 crore for children’s additional obligations and ₹50 crore for other breaches. These are selected ceilings, not automatic fines. The Board considers the breach and statutory factors after an inquiry. See section 33 and the Schedule of the Act.
Budget for a well-defined implementation because connected workflows, clear ownership and testable requirements matter. A software purchase alone should not be presented as a guarantee of compliance.
Improve what you have, or build something new?
Start by checking whether your existing tools can support the approved workflow. If they expose suitable APIs and usable preference fields, an integration may be practical. If an important journey has no usable interface or record structure, a custom component may be needed.
Compare the options using integration effort, operational ownership, security review, maintenance and rollout disruption. Avoid replacing a business-critical application before understanding the actual gap.
Turn your DPDP requirements into a technical plan
Scrupulous Technology can scope and develop consent interfaces, preference records, withdrawal workflows and integrations with existing applications, based on your approved requirements.
Explore our DPDP consent management system development service. For a useful first discussion, bring your system list, one customer journey and the teams responsible for approval.
Frequently asked questions
Does every use of personal data require consent?
No. The Act recognises consent and certain legitimate uses. Have your legal adviser identify the appropriate ground for each use case before configuring a consent workflow.
Is a consent management system a registered Consent Manager?
Not necessarily. A registered Consent Manager has a specific statutory role. Custom software supporting a company’s workflows does not automatically confer that status. Scrupulous Technology’s service is custom development and integration.
Can we keep our existing CRM and mobile app?
Possibly. The decision depends on the approved requirements, available interfaces and data model. Review a real journey and the integration constraints before deciding.
How long will implementation take?
Timing depends on the number of journeys, systems, approval cycles and test scenarios. A scoped review is needed before quoting a delivery schedule.
Reviewed 11 October 2026. Technical planning guidance; legal applicability and policy decisions require your advisers’ review.